Contact Us:
MoD Cyber Security Model
UK Ministry of Defence Cyber Security Model (CSM v4)
MoD DSC Model (CSMv4), Standards and Guidance
The UK Ministry of Defence issued an Industry Security Notification (ISN) on the 26th November 2025, updating the CSM to change its focus from MoD Identifiable Information to organisational security and resilience. Confirming the effective date of its Cyber Security Model Version 4 (CSM v 4) of the 3rd December 2025 (ISN 2025/ 07). The ISN applies to all suppliers engaged on contracts for which the UK MOD is a contracting party, or subcontracts.
CSM 4 is the MoD’s risk-based framework for managing supply chain security. It is the overarching system used by the MoD to enable its suppliers to assess cyber risk across the defence supply chain and assigns suppliers to specific Cyber Risk Profiles (Level 0 through Level 3) that the MoD requires suppliers to maintain to comply with supplying the MoD.
The MoD’s CSM v4 cybersecurity requirements are a significant departure from historic MoD cyber requirements and clearly adopt an approach similar to the US Department of Wars Cybersecurity Maturity Model Certification Program (CMMC), which is regulated under US Defence Federal Acquisition Regulation (DFARS), 252.204-7012, and 7021.
Compliance with the defined Cyber Risk Profile is evaluated through an independent assessment and is used to evidence that a defense contractor operates the required controls defined in DefStan 05-138.
The MoD Cyber Security Modelv4 Process
All contractors and subcontractors that supply the UK MoD are required to comply with CSMv4 for new and existing procurements. It shifts the focus from “MOD Identifiable Information” to organisational security and resilience, introduces four Cyber Risk Profiles (Levels 0 to 3), and uses the cybersecurity controls set out in Def Stan 05-138 Issue 4. Covered organisations are required to self-assess their compliance with the cybersecurity controls The process for a supplier, defined by the CSMv4.
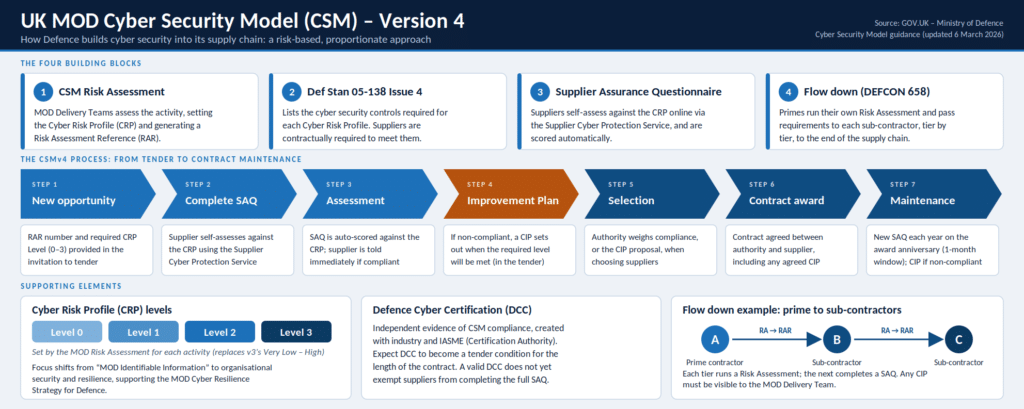
Figure 1: The MoD Cyber Security Modelv4 process
All contractors and subcontractors that supply the UK MoD are required to comply with CSMv4 for new and existing procurements. It shifts the focus from “MOD Identifiable Information” to organisational security and resilience, introduces four Cyber Risk Profiles (Levels 0 to 3), and uses the cybersecurity controls set out in Def Stan 05-138 Issue 4. Covered organisations are required to self-assess their compliance with the cybersecurity controls. The process for a supplier is defined by CSMv4.
- Risk Assessment Reference and required Cyber Risk Profile. The authority provides a Risk Assessment Reference (RAR) number and the Cyber Risk Profile (CRP) level (0 to 3) at the earliest market engagement, usually in the invitation to tender. The profile comes from the MOD delivery team’s risk assessment.
- Complete the Supplier Assurance Questionnaire (SAQ) in the Supplier Cyber Protection Service (SCPS). Organisations wishing to bid for an MoD Contract are required to complete a SAQ. The SAQ is a self-assessment against the required profile through the SCPS. The SAQ is scored automatically against the profile, and you are told immediately whether you are compliant.
- Organisations that do not comply with the MoDs Cyber Risk Profile. Submit a Cyber Improvement Plan (CIP) to the MoD. The CIP identifies the gaps and activities the organisation will undertake to comply with the CRP. The plan includes compliance dates with timescales, or gives reasons why you can’t comply. It becomes part of the contract and should be included in your tender.
- Flow down to subcontractors. The MoD requires Prime contractors to flow down Cyber Risk Profile requirements to lower-tier sub-contractors and onwards down the sub-contracting tiers to the end of the supply chain. If a subcontractor is non-compliant, a Cyber Improvement Plan must be agreed between the parties, and the MOD delivery team must be able to see it. DEFCON 658 sets out the contractual terms, including the cyber security requirements that must be placed on subcontractors.
- The MoD/ Prime/ Contractor considers and organisations compliance and CIP proposal, when selecting suppliers. Any agreed CIP goes into the contract.
- MoD Suppliers complete a new SAQ on each anniversary of contract award, with a one-month window afterwards. If you are non-compliant, a CIP is required.
CSMv4, Risk Assessment
The MoD Delivery Team (the authority) completes the initial RA for a new or existing MoD activity. Suppliers do not self-select their level. The authority provides a Risk Assessment Reference (RAR) and the required CRP level, usually at the earliest market engagement and typically in the invitation to tender. The MoD provides a Risk Assessment Reference and required Cyber Risk Profile level relevant to a new or existing MOD activity, usually found in the invitation to tender. The same supplier can therefore get different levels on different contracts.
Assessments are completed in the online Supplier Cyber Protection Service (SCPS). Completing a short question set (six key questions) examining the cyber risk linked to the supplier’s role in the supply chain. A Cyber Security Profile is assigned based on the risk. There are 4 Cyber Security Profile Levels.
- Level 0, (‘Basic’) – Low Risk – 3 Controls – Assigned where there is a very low level of assessed cyber risk to a Supplier delivering an output. It requires Supplier organisations to demonstrate basic cyber security practices.
- Level 1, (‘Foundational’) – Low to Moderate Risk – 101 Controls – Assigned where there is a low to moderate level of assessed cyber risk to a Supplier delivering an output. It requires Supplier organisations to demonstrate a comprehensive cyber security programme with good practices.
- Level 2, (‘Advanced’) – High – 139 Controls – Assigned where there is a high level of assessed cyber risk to a Supplier delivering a contracted output. It requires Supplier organisations to demonstrate advanced cyber security oversight and planning, which drives robust organisational and cyber practices.
- Level 3 (‘Expert’) – Highest – 144 Controls – Assigned where there is a substantial level of assessed cyber risk from a Supplier delivering a contracted output. It requires Supplier organisations to demonstrate expert cyber security capabilities that fully take advantage of the ‘defence in depth’ methodology to appropriately protect the organisation against new and evolving threats.
