 Call us now:
Cyber Governance and Regulatory Compliance
Get advice from experienced Cybersecurity, Governance, Risk and Compliance professionals
Advice and Support
Cybersecurity and regulatory compliance can be complex and challenging to navigate. Expert advice and practical support can help organisations understand their obligations, manage risk and achieve effective compliance. Partial, incorrect or inadequate compliance can result in lost contracts, corporate and personal fines, reputational damage and, in serious cases, criminal liability and imprisonment.
Get Advise
We provide independent, practical advice and guidance across cybersecurity, risk management, governance and regulatory compliance. Our advice is grounded in more than 25 years of experience delivering 1st and 2nd Line of Defence cybersecurity and regulatory services, supporting organisations in navigating complex cyber requirements, and advising regulators. Whether you need strategic direction, help understanding your regulatory obligations, or practical support in addressing a specific cybersecurity or compliance challenge, we provide experienced, actionable advice tailored to your organisation’s needs.
Work With Professionals
Professional expertise, credibility and high standards are fundamental to effective cybersecurity and regulatory compliance. As regulatory expectations continue to increase, organisations must be able to demonstrate that cybersecurity and risk decisions are informed, competent, consistent and supported by appropriate professional judgement. We work with professionals and organisations to strengthen capability, provide expert guidance and support the consistent application of recognised cybersecurity, governance, risk and regulatory standards.
Compliance
Cybersecurity regulatory compliance is essential to demonstrating that an organisation is effectively identifying, managing and overseeing cyber risk in line with applicable legal, regulatory and professional standards. Effective compliance goes beyond simply meeting requirements—it requires clear governance, appropriate oversight, reliable assurance and evidence that cybersecurity risks are being actively managed and controlled.
Articles and Publications
We have produced an extensive body of articles, papers, strategies and thought-leadership publications, alongside webinars and conference contributions, covering cybersecurity, risk management, governance and regulatory compliance. Our work draws on practical experience across legal and regulatory requirements, cyber governance, organisational risk and cybersecurity, providing informed perspectives and practical guidance for professionals and organisations.
Largest Balance Sheet
0
€B
Years Security Experience
0
Professional Accreditions
0
Leadership Roles
0
Practice Areas
Cybersecurity regulation is expanding rapidly across jurisdictions, creating increasingly complex legal, regulatory and compliance obligations for organisations. Our practice areas cover key cybersecurity and regulatory frameworks across the United States, European Union and United Kingdom, including EU NIS2, DORA, SEC Cybersecurity Disclosure Rules, US DoD DFARS/CMMC, and the UK Cyber Security and Resilience Bill.
We provide practical guidance to help organisations understand their obligations, assess compliance requirements, manage cyber risk and strengthen governance and assurance, while recognising the potentially significant civil, regulatory and, in some circumstances, criminal consequences of non-compliance.
Corporate Governance
We help boards and senior leaders strengthen governance, oversight and assurance over cybersecurity risk. Our approach supports informed decision-making, clear accountability and effective risk management, while helping organisations demonstrate compliance with applicable legal, regulatory and professional requirements.
Regulatory Compliance
We help organisations understand, implement and demonstrate compliance with US and EU cybersecurity regulations. Our approach provides practical guidance on navigating complex regulatory requirements, assessing compliance obligations and strengthening governance, risk management and assurance.
Cybersecurity
We help organisations manage cybersecurity and compliance programmes, providing practical advice and support to meet regulatory requirements, manage cyber risk and strengthen governance.
Risk Management
We help organisations navigate DFARS/ CMMC compliance requirements, supporting the international Defence Industrial Base (DIB) in managing complex US cybersecurity obligations. We support organisations in establishing effective compliance programmes and controls, helping protect sensitive information, meet DFARS/ CMMC requirements, and maintain access to US Department of Defense contracts.
Artificial Intelligence (AI)
We help organisations manage AI-related cybersecurity and intellectual property risks, supporting boards and management in understanding, assessing and governing emerging threats. We support organisations in establishing effective AI governance, risk controls and security measures, helping protect sensitive information, intellectual property and critical business assets.
DFARS/ CMMC
We help organisations understand and manage DFARS/ CMMC compliance requirements, supporting the international Defence Industrial Base (DIB) in navigating complex US cybersecurity and contractual obligations. We support organisations in establishing effective compliance programmes, security controls and assurance, helping protect sensitive information, meet DFARS/ CMMC requirements and maintain eligibility for US Department of War contracts.
Oversight & Assurance
We help boards demonstrate effective oversight and assurance of cybersecurity risk management, supporting governance, accountability and reporting. We support boards in implementing appropriate target operating models, committee structures, oversight and assurance, helping ensure cybersecurity risks are effectively governed, challenged and monitored.
Who Is Parava
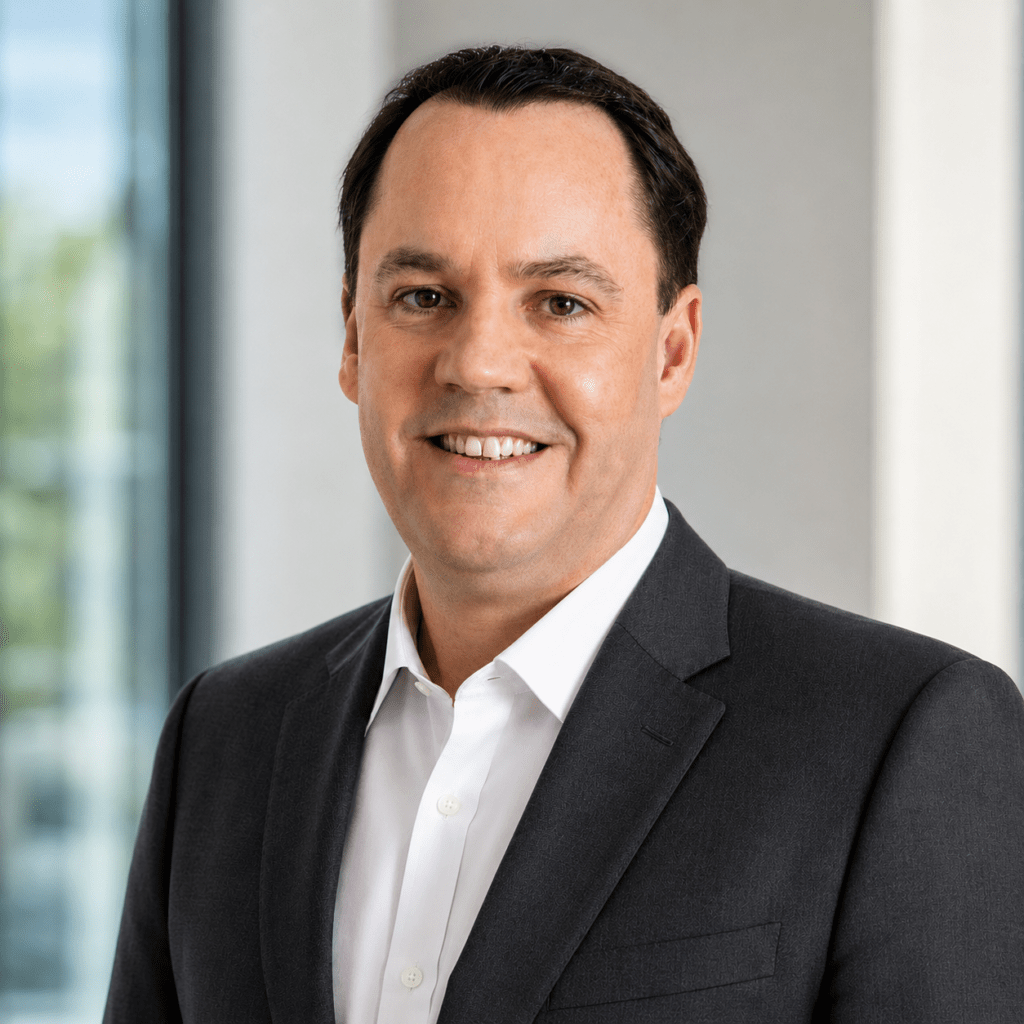
Andy Watkin-Child
Founding Partner
I am a 25-year veteran of Regulatory Compliance, Board Governance, Risk Management, and Cyber Security. I have built and led both the 1st and 2nd Line of Defence cybersecurity and risk management for regulated companies across Engineering, Financial Services, Media and Publishing, and financial statements up to €1.4 trillion.
I received a U.S. President Volunteer Services Award for my work as a plank member of the U.S DoD CMMC program. I hold Chartered Security Professional (CSyP) and Chartered Engineer (CEng) status, and I am an assessor for membership of the Register of UK Security Professionals.
Cybersecurity, risk management, governance, and regulatory compliance are what I do, and I provide Boards with the tools so that they may progress on their cyber regulator compliance journey.
Andy Watkin-Child
Arrange a Conversation
Office
36 Crescent Road
Bishopstone
Worthing
West Sussex
BN11 1RL
Contact
contact@parava.org
Open Hours
Monday-Saturday 8 am - 6pm
Sunday 11am - 4pm