Contact Us:
MoD – Def Stan Level 3
Def Stan 05-138 Cyber Security Profile Level-3
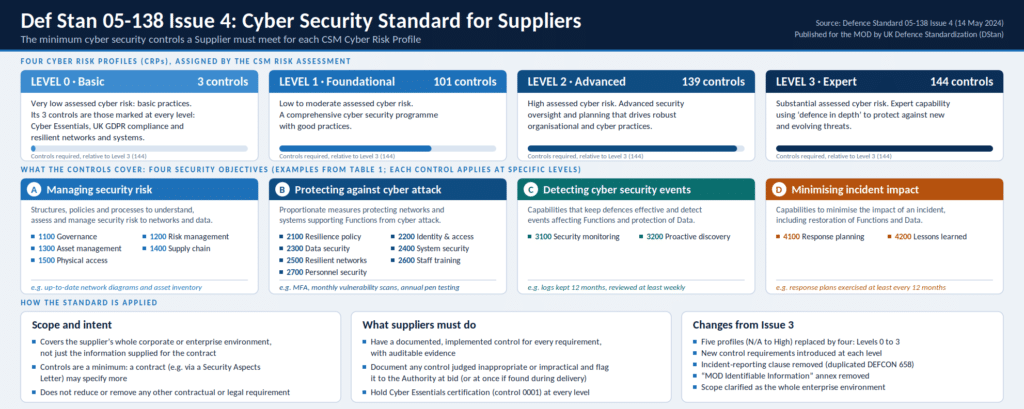
MoD DSC Model (CSMv4), Cyber Security Profile Level-3
Def Stan 05-138 Level 3 (Expert) is the highest Cyber Risk Profile within the UK Ministry of Defence’s Cyber Security Model (CSM). It is normally assigned to suppliers assessed as presenting a substantial level of cyber risk when delivering contracted outputs. Level 3 comprises 144 cyber security controls and requires organisations to demonstrate expert cyber security capabilities, using a defence-in-depth approach to protect against new and evolving threats. The standard takes a whole-organisation approach, requiring suppliers to protect their corporate environment, including people, systems, processes, infrastructure, data and supply chain dependencies. Its objective is to ensure that suppliers can maintain the resilience of their operations while protecting UK and Partner Data.
Level 3 builds on the foundational and advanced requirements, demanding a more sophisticated and comprehensive approach to cyber security. This includes strong governance and risk management, tightly controlled identities and privileged access, robust data protection, secure system architecture, continuous security monitoring, vulnerability management and effective incident response. A central requirement is the ability to anticipate, detect and respond to sophisticated and emerging cyber threats. Organisations must apply defence-in-depth principles, ensuring that multiple complementary security measures protect critical systems and information, rather than relying on individual controls.
Level 3 places particular emphasis on the use of threat intelligence to inform security architecture, system development, monitoring, threat hunting, security alerts and incident response. It also requires enhanced assurance of security controls and the ability to demonstrate that protective measures remain effective. Organisations operating at this level must be capable of identifying weaknesses, responding to incidents, learning from security events and improving their defences. The objective is to provide a high level of resilience against sophisticated cyber threats and protect the continuity of defence-related operations.
Level 3 therefore represents the most demanding level of the standard, requiring expert capabilities, proactive threat management and a mature, integrated approach to cyber security across the organisation.
Def Stan 05-138 Level 3 (‘Expert’) – 144 controls (138 Level 0, Level 1, Level 2 controls plus 6 Level 3 Controls)
Def Stan 05-138 Level 2 (‘Advanced’) – Additional Level 2 Controls
| ControlID | Control Name | Control Requirement |
|---|---|---|
| 1204 | Threat intelligence capabilities | The Supplier shall implement threat intelligence capabilities (internally or externally) as part of a risk assessment to guide and inform the development of organisational systems, security architectures, selection of security solutions, monitoring, threat hunting, system security alerts and advisories, response and recovery activities. |
| 2209 | Limit access to authorised entities | The Supplier shall implement automated mechanisms to support the management of system accounts, including processes acting on behalf of authorised users. |
| 2415 | Automatically identify and address misconfigurations and unauthorised components | The Supplier shall employ automated mechanisms to detect misconfigured or unauthorised system components. |
| 2425 | Use integrity verification tools | The Supplier shall implement an integrity verification tool to detect unauthorised changes to web-facing, critical software and firmware. Upon discovering discrepancies, the tool should automatically trigger the incident response process. |
| 3102 | Continuously monitor security controls | The Supplier shall establish and document security event monitoring which at a minimum covers the following: i) 24x7x365 monitoring of all identified Information Systems in Production and non-Production environments ii) Tools used for 24x7x365 monitoring and correlation iii) Security events covered iv) Frequency of monitoring v) Clearly defined roles and responsibilities vi) Escalation matrix. |
| 4202 | Operation resilience for equipment | The Supplier shall assess the requirement for redundant networking and telecommunication systems to protect Functions and Data. Where required, the Supplier shall implement and protect these systems. |
