Contact Us:
MoD – Def Stan 05-138
UK Ministry of Defence Supplier Cyber Security Standard 05-138
The Cyber Security Standard for all MoD Suppliers
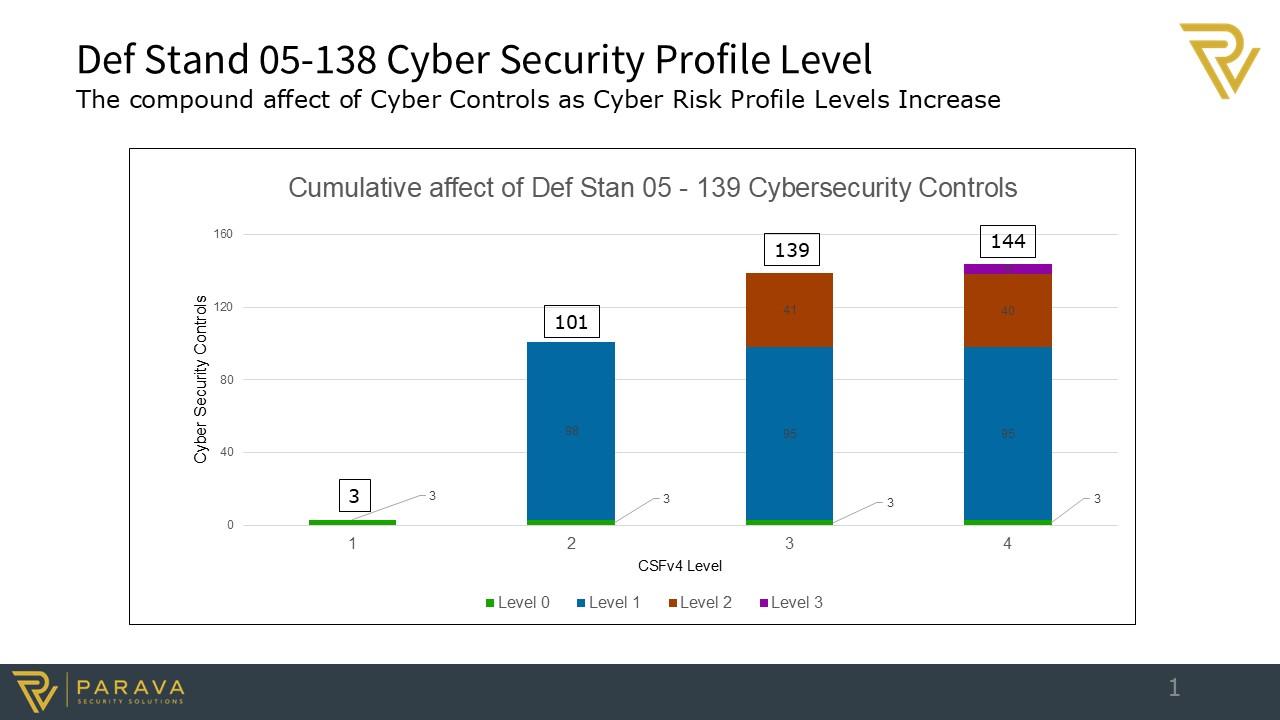
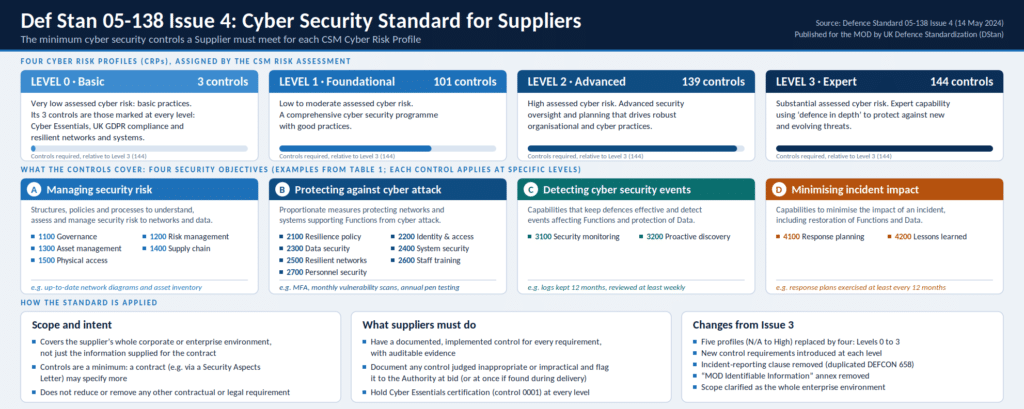
UK Ministry of Defence Standard 05-138 (Def Stan 05-138 – Cyber Security Standard for Suppliers) is the UK Ministry of Defence’s cyber security standard for suppliers. Issue 4 published on 14 May 2024 by the MoD, underpins the Cyber Security Model (CSM), the MOD’s risk-based and proportionate approach to strengthening supplier resilience and protecting data. The standard defines the CSM’s Cyber Risk Profiles and the minimum controls a supplier must meet for each. Issue 4 replaced the earlier five profiles with four: Level 0 (Basic, 3 controls), Level 1 (Foundational, 101), Level 2 (Advanced, 139) and Level 3 (Expert, 144). The CSM Risk Assessment assigns the profile for a given contract.
The scope of Def Stan 05-138 is the supplier’s whole corporate or enterprise environment, not just the information provided for a contract. The controls are organised under four objectives: managing security risk, protecting against cyber attack, detecting cyber security events, and minimising the impact of incidents. They cover areas such as governance, access control, data protection, monitoring and incident response. Suppliers must have each required control documented and implemented, with auditable evidence. Controls judged impractical must be documented and flagged to the Authority. The requirements are a minimum, so individual contracts may demand more, and the standard doesn’t reduce any other legal or contractual obligations.
- The Cyber Security Model (CSM) is a risk-based, proportionate approach to strengthening Supplier resilience, and protecting UK & Partner Data as it moves through, or is generated in, the supply chain.
- The CSM seeks to adopt a whole enterprise/organisational approach to cyber resilience that ensures its continued operation and delivery of its contracted output and protection of Data, including that of the UK and its International Partners.
- This Defence Standard defines the CSM Cyber Risk Profiles and associated minimum cyber
security control requirements of a Supplier organisation.
Scope of Def Stan 05-138
Def Stan 05-138 applies to the entirety of a MoD supplier’s corporate or enterprise environment. All Supplier organisations, systems, processes, procedures and data necessary for their effective protection of Data and/or Functions are within the scope of this standard, going beyond the protection of just the information provided to the Supplier in support of that contracted output. The standard is, therefore, intentionally broad, ensuring that a Supplier organisation, irrespective of any controls required for a specific contracted output, has the appropriate minimum levels of controls in place for the level of risk to which that Supplier organisation is expected more generally.
- The requirements set out within this standard are derived from current international and industry best practices, as well as requirements placed upon the MOD as a UK Government department.
- These requirements are intended to be considered as a ‘minimum’. Individual contracts may specify greater levels of controls/protection (such as where specified within a Security Aspects Letter).
- It is intended that this standard will be regularly reviewed and updated, to ensure its continued currency and fit for purpose.
- This standard may not be taken as a basis to reduce or remove any other requirements placed upon a Supplier organisation, whether contractual or legal.
Def Stan 05-138 – Cyber Security Profiles
The Cyber Security Model Risk Assessment Process assigns a Cyber Risk Profile (CRP) to a given risk profile. The CSM Cyber Risk Profiles are defined across 4 levels.
- Level 0 (‘Basic’) – 3 controls – The Level 0 ‘Basic’ CRP is normally assigned where there is a very low level of assessed cyber risk to a Supplier delivering an output. It requires Supplier organisations to demonstrate basic cyber security practices.
- Level 1 (‘Foundational’) – 101 controls – The Level 1 ‘Foundational’ CRP is normally assigned where there is a low to moderate level of assessed cyber risk to a Supplier delivering an output. It requires Supplier organisations to demonstrate a comprehensive cyber security programme with good practices.
- Level 2 (‘Advanced’) – 139 controls – The Level 2 ‘Advanced’ CRP is normally assigned where there is a high level of assessed cyber risk to a Supplier delivering a contracted output. It requires Supplier organisations to demonstrate advanced cyber security oversight and planning which drives robust organisational and cyber practices.
- Level 3 (‘Expert’) – 144 controls – The Level 3 ‘Expert’ CRP is normally assigned where there is a substantial level of assessed cyber risk from a Supplier delivering a contracted output. It requires Supplier organisations to demonstrate expert cyber security capabilities that fully take advantage of the ‘defence in depth’ methodology to appropriately protect the organisation against new and evolving threats.
Def Stan 05-138 requires covered contractors to comply with the cybersecurity controls defined in the standard for each level. They are required to demonstrate their oversight and assurance of the controls with evidence.