Contact Us:
MoD – Def Stan Level 0
Def Stan 05-138 Security Profile Level-0
MoD DSC Model (CSMv4), Cyber Security Profile Level - 0
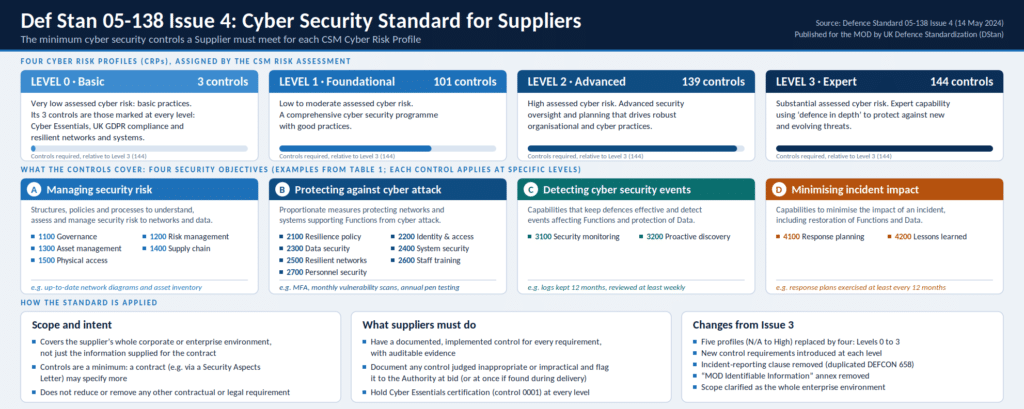
Defence Standard 05-138 Issue 4 defines Cyber Risk Profile (CRP) Level 0 as the Basic level of cyber security assurance within the MOD’s Cyber Security Model (CSMv4). It is normally assigned to suppliers where the assessed cyber risk associated with delivering goods or services to Defence is considered very low.
Level 0 requires organisations to demonstrate three basic cyber security controls, establishing a minimum level of protection against common and untargeted cyber threats. The requirements include maintaining Cyber Essentials certification and demonstrating appropriate basic cyber security practices, including compliance with applicable data protection requirements.
Although Level 0 has relatively limited control requirements compared with higher profiles, it is not an exemption from cyber security responsibilities. Suppliers must ensure that the required controls are documented, implemented and supported by auditable evidence.
The Ministry of Defence determines the appropriate Cyber Risk Profile through its contractual risk assessment process. Suppliers must complete the relevant Supplier Assurance Questionnaire (SAQ) to demonstrate compliance. Where requirements cannot be met, a Cyber Improvement Plan may be necessary, subject to agreement with the MOD.
Level 0 provides a proportionate baseline for suppliers undertaking low-risk Defence activities, helping establish confidence that organisations have fundamental cyber security protections in place and can contribute to a more resilient Defence supply chain.
Def Stan 05-138 Level 0 (‘Basic’) – 3 controls
| Def Stan 05-138 Control ID | Control Name | Level 0 | Control Requirement |
|---|---|---|---|
| 1 | Cyber Essentials | Yes | The Supplier shall have Cyber Essentials certification that covers the scope required for all aspects of the contract and commit to maintaining this for the duration of the contract. |
| 2314 | Ensure UK GDPR compliance | Yes | The Supplier shall ensure that the processing of personal data is conducted in compliance with the General Data Protection Regulation. |
| 2500 | Resilient networks and systems | Yes | The Supplier shall build resilience against cyber-attack and system failure into their design, implementation, operation and management of systems that support the operation of business Functions and protection of Data. |
